Safe AI Is More Than a Filter: Why AI Risk Is a Business Problem
October 19, 2026 · Webcure Insights
The most serious AI risk is not a bad answer. It is what people do when they trust that answer.
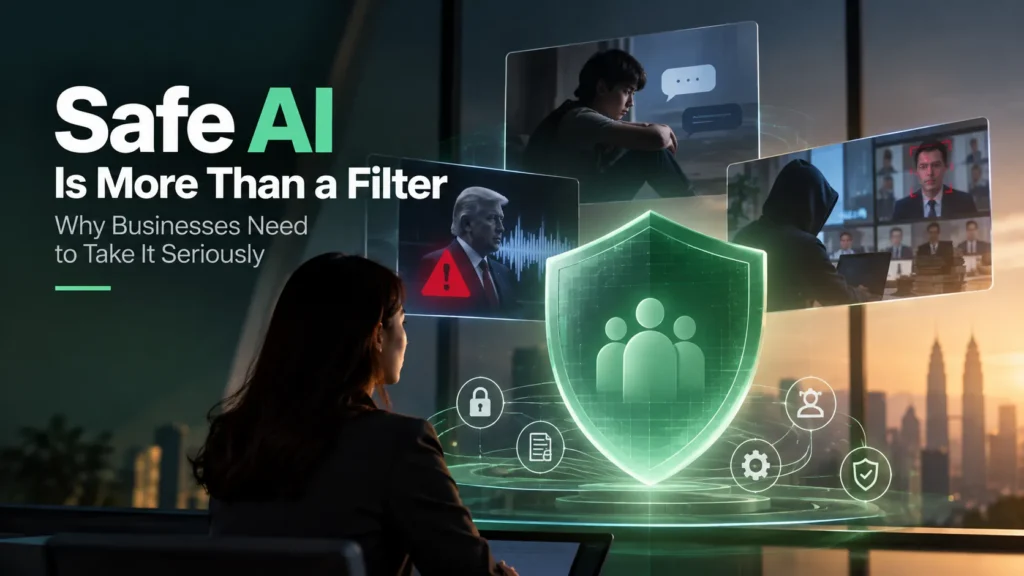
An AI companion can respond badly to someone in distress. A convincing deepfake can persuade an employee to approve a transfer. An AI application can reach information it was never meant to see. These are different failures, but they begin in the same place: AI deployed without enough control.
When the consequences are real
Human safety and wellbeing
In 2024, a 14-year-old died by suicide after using an AI companion. His mother alleged that the chatbot contributed to his death. In January 2026, Google and Character.AI agreed to settle the lawsuit. The settlement did not establish through a court judgment that the chatbot caused the death.
The case still raises serious questions about the responsibility of organisations that put AI companions in front of children and vulnerable users.
Misinformation and public trust
During the 2024 New Hampshire primary, an AI-generated imitation of President Joe Biden’s voice was used in robocalls that discouraged people from voting. The US Federal Communications Commission later issued a US$6 million fine against political consultant Steve Kramer over the campaign.
The problem was not simply that the audio was false. It was synthetic media used deliberately to mislead people and weaken confidence in public communication.
Source: US Federal Communications Commission, September 2024
Fraud and cybersecurity
In 2024, an employee in Arup’s Hong Kong office approved transfers worth HK$200 million — about US$25.6 million — after a video call featuring AI-generated versions of senior colleagues. Arup confirmed it was the victim of fraud and said its internal systems had not been compromised.
The lesson is that AI-enabled fraud does not always require a technical breach. It can exploit human trust, impersonation and weak approval processes.
Source: The Guardian, May 2024
Safety is an operating responsibility
Safe AI means designing, deploying and managing AI systems to reduce foreseeable harm to people, organisations and society across the whole lifecycle. It is broader than filtering bad content.
An AI system can refuse offensive questions and still be unsafe if it exposes confidential information, gives misleading advice, enables fraud or acts beyond its intended authority.
Frameworks such as the NIST AI Risk Management Framework and the OECD AI Principles point to risk management, security, accountability and continuing assessment. A reputable model provider does not automatically make the application built around that model safe.
Source: NIST AI Risk Management Framework | OECD AI Principles
A practical baseline
Organisations do not need to eliminate every conceivable risk before they start. They do need a defensible foundation.
- Understand the risks. Define what the AI may do, who could be affected and what could go wrong.
- Protect data and access. Limit the information the AI can see and the actions it can take.
- Test for failure. Look for inaccurate output, harmful responses, privacy exposure, manipulation and other realistic failure scenarios before launch.
- Keep humans accountable. Important decisions need review, escalation and a route to challenge the outcome.
- Monitor and respond. Review behaviour, investigate incidents and be ready to correct, suspend or disable the system.
The level of control should match the level of risk. An internal writing assistant is not the same as an agent that can read customer records or initiate payments.
No set of controls removes all risk. The goal is to identify foreseeable harm, reduce its likelihood and impact, and respond well when something goes wrong.
Responsible adoption is the goal
Innovation and safety are not opposites. Deploying AI without understanding its risks is not responsible innovation either.
A capable model can produce impressive answers. Trust depends on the data it receives, the systems it can reach, the permissions it has, how it is tested and who remains accountable for its actions.
Safe AI is not about making AI less useful. It is about making it useful without exposing people and organisations to avoidable harm.
As AI moves from experiments into everyday operations, safety has to be part of the architecture, the governance and the culture — not a final check before launch.
- AI risk starts when people act on an answer they trust.
- Controls need to cover content, data, permissions, people and monitoring.
- Safety belongs in the design and operation of the system, not at the end of the project.
Want to talk about this?
This article describes work we do every day. Let’s apply it to your business.